
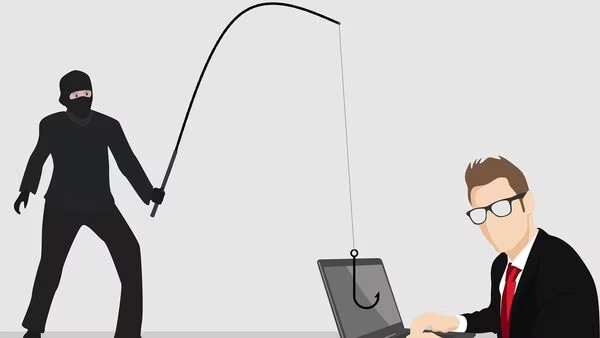
KYC fraud is a growing cyber threat, where scammers impersonate bank officials to trick users into revealing sensitive data under false pretenses—often disguising it as urgent account verification. Targets are lured via phishing SMS messages containing malicious links or fake APKs that, once installed, can steal OTPs, CVV numbers, contact lists, and more. Major banks like ICICI, Axis, and HDFC have warned that they never ask for KYC updates via such links or apps.
These fraudulent APKs typically bypass official app stores, making detection difficult while quietly harvesting data or even controlling devices remotely. Cybersecurity agencies—such as CERT-In—continue to alert users to these serious Android, iOS, and browser vulnerabilities.

"Leading banks such as ICICI Bank, Axis Bank and HDFC Bank have reiterated that they never request KYC updates via third party applications or SMS links."
To stay safe, always avoid clicking on unsolicited links or installing apps from unofficial sources. Never share your OTP, CVV, or PIN over messages or calls. Stick to official banking applications and websites for any KYC or account updates. If suspicious activity arises, report it immediately to the National Cyber Crime Helpline (1930) or www.cybercrime.gov.in, or forward phishing attempts via Sanchar Saathi or directly to your bank’s fraud email.
Post A Comment
Sign in to post your comment or signup if you don't have any account.